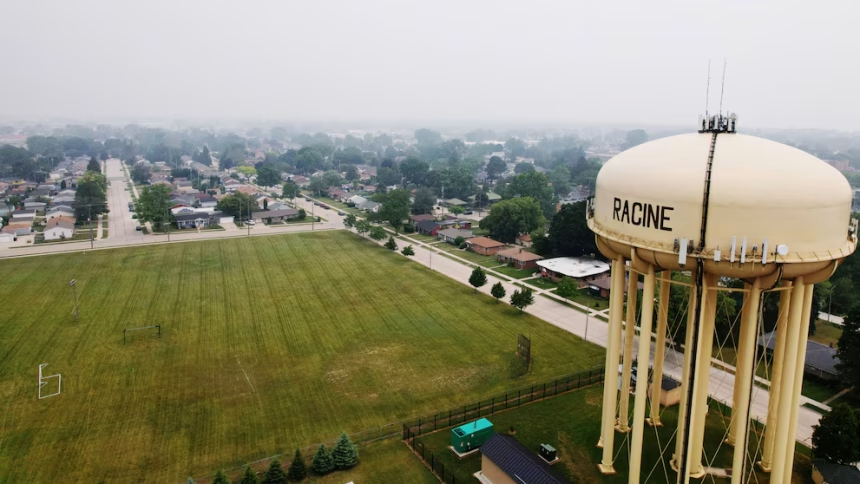
If you’re someone who turns on the faucet to pour a glass of water with complete trust—assuming the worst you’ll find is a little chlorine—recent news shaking the U.S. will force you to rethink that basic sense of security. The truth is, in the era of digital warfare, the battlefield is no longer just remote military bases or Pentagon servers; it’s the critical infrastructure that keeps the civilian population alive.
We’re talking about a series of sophisticated cyber intrusions that have breached the industrial control systems of drinking water treatment and distribution plants in at least seven U.S. states. Even more alarming, federal intelligence and national security agencies point, with a high degree of certainty, to Iran as the primary suspect behind this coordinated offensive. But what exactly are these hackers after? Are we facing a real danger to public health, or is this just a digital show of force by a geopolitical adversary?

The Threat at a Glance (Snippet Bait): Targeted cyberattacks have compromised the operational security of drinking water systems in seven U.S. states, triggering federal alarms. Cybersecurity officials identify agents linked to the Iranian government as the perpetrators of these hacks, which exploit vulnerabilities in outdated control equipment. While no mass contamination has been reported, the ability to alter water chemical levels poses a latent threat to the public health of millions of citizens.
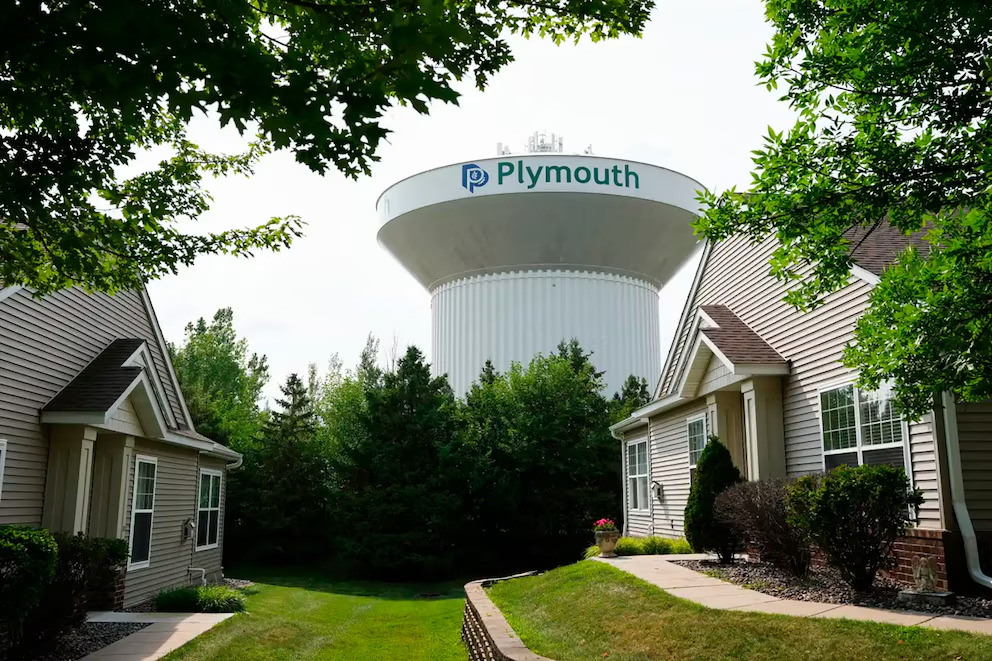
The Anatomy of the Hack: How Was the Water Compromised?
To grasp the magnitude of this crisis, you have to look beyond the computer screen. Modern water systems don’t operate on their own; they’re managed by complex Supervisory Control and Data Acquisition (SCADA) systems.
1. The Achilles’ Heel: Programmable Logic Controllers (PLCs)
The attackers didn’t try to poison the water directly by typing commands into a central console in Tehran. Their method was more insidious: targeting the peripheral components that regulate flow, pressure, and chlorine levels.
- The security breach: Hackers gained access to programmable logic controllers (PLCs) from a specific brand (Unitronics) commonly used in small and medium-sized water plants. Why? Many of these facilities operate with default factory passwords or are connected directly to the internet without robust firewalls, making them open doors for any digital intruder with basic knowledge.
- The modus operandi: Once inside, the attackers could alter configurations, turn pumps on or off, and in at least one documented incident in a Pennsylvania municipality, they managed to manipulate the control screen to the point of forcing the system to shut down completely, displaying anti-Israel messages—a clear signature of the alleged Iranian origin.
2. The Geopolitical Factor: Why Now and Why Water?
Pointing to Iran is neither coincidental nor a conspiracy theory. The U.S. intelligence community (CISA, FBI, NSA) has issued joint alerts warning about the activity of Iranian cyber groups (such as the self-proclaimed “Cyber Av3ngers”).
- Digital retaliation: These attacks appear to be direct retaliation for U.S. support of Israel in the Gaza conflict. Iran, a long-standing U.S. rival and sponsor of anti-Israel groups, has intensified its asymmetric warfare in cyberspace.
- Targeting soft spots: Attacking water plants doesn’t require a billion-dollar military budget, but it generates mass psychological terror and demonstrates the ability to harm the U.S. civilian population without crossing a kinetic warfare threshold that would justify a traditional military response. It’s the perfect definition of aggression in the “gray zone.”
Impact Table: A State-by-State Vulnerability Breakdown
To help you visualize the geographic scope of this issue, we’ve synthesized official reports on the affected states and the nature of the incidents.

| State Affected | Nature of Incident / Threat | Population Risk | Federal Alarm Level |
| Pennsylvania | Intrusion at a municipal water plant; alteration of a controller’s graphical interface. | High in the affected locality due to operational shutdown. | Very High (CISA issued a specific alert) |
| New York | Detection of suspicious activity in rural water district systems. | Potential, mitigated by early detection. | High |
| Indiana | Intrusions targeting water and energy infrastructure. | General | High |
| Illinois | Compromise of remote control systems in treatment plants. | General | High |
| North Carolina | Exploratory activity and vulnerability scanning in water networks. | Low to Moderate (preventive) | Moderate |
| New Jersey | Confirmed intrusions in municipal SCADA systems. | General | High |
| Texas | Unspecified reports of cyber incidents at water plants. | General | Moderate |
(Note: This table is based on public information and government agency reports as of the date of publication. The number of affected states may increase as investigations progress.)
Practical Guide: What Should Your Family Do in Response to This Alert?
In the face of uncertainty, information and preparation are your best defenses. This isn’t about panicking—it’s about acting smartly.
- Stay informed through official sources, not social media! In crisis situations, social media fills up with rumors and misinformation designed to create chaos. If your water system is compromised, local authorities (your municipality, the public health department) have a legal and operational obligation to issue immediate alerts (e.g., “boil water”). If you haven’t received an official alert, assume the water is safe for human consumption. Trust only communications from government sources (.gov) or trusted local news outlets.
- Demand transparency from your local water provider. As a citizen and taxpayer, you have the right to know what security measures protect your water supply. Call your water company or ask at your next city council meeting: “Does our plant operate with internet-connected SCADA systems? Have the factory-default passwords been changed? Is there a cyberattack response plan?” Public pressure drives investment in security.
- Basic emergency preparedness never hurts. Regardless of cyberattacks, having a household emergency plan is prudent. Federal emergency management agencies (FEMA) recommend storing at least one gallon of water per person per day for at least three days, for both drinking and hygiene. Keeping a small stock of bottled water will give you peace of mind in case of any service disruption, whether due to hacking, a natural disaster, or an accident in the network.
The truth is that cyberattacks on U.S. drinking water systems have gone from a hypothetical horror-movie scenario to an uncomfortable and dangerous reality. Pointing to Iran as the primary suspect underscores the complexity of modern global threats. For our Hispanic community, this means that security is no longer just about locking your front door—it’s also about demanding that the public infrastructure supporting our daily lives is defended with the utmost seriousness on the digital front. We will continue monitoring this critical situation to bring you the unvarnished truth without alarmism.

Image: ElHispanoParaTodos/PRESS